Everything under the hood
37 built-in auditors and 52 wrapped scanners, merged into one scored report. Run it from your terminal, your CI or your agent.
bunx @openaudit/cli .Built for agents
Your agent runs the audit, fixes what it finds and checks the fix.
MCP server
For Claude Code, Cursor, Codex and more. Over stdio or HTTP.
10 playbooks
For checks that need judgment. Your agent runs them, no extra API key.
JSON mode
--jsonprints one report and nothing else.Agent skill
SKILL.mdteaches the audit, fix, verify loop.
claude mcp add openaudit -- bunx @openaudit/cli mcp- Audit this project with openaudit (https://openaudit.se/llms.txt). Fix what matters most, then run it again to check.
- openaudit run_audit target: "."
- 78/100, grade C. 1 critical and 3 high findings from 41 auditors.
- openaudit get_playbook id: "agent.authz"
- Authentication and authorization review: inventory every route, then check who can reach it.
- Read src/routes/admin.ts
- openaudit submit_findings 2 findings
- Merged into the report. Security 61 to 54.
- Edit src/routes/admin.ts, src/config.ts
- openaudit compare_reports
- 3 fixed, 0 new.
Ten areas, each with its own grade
Every finding lands in one area. Each area gets a 0 to 100 score.
Security
Secrets, risky code, TLS and headers, exposed files, container and cloud config.
src/config.ts:14code.secrets/aws-access-key-idWrapped tools
- semgrep
- trivy
- gitleaks
- osv-scanner
- trufflehog
- checkov
- zizmor
- grype
- bandit
- gosec
All 34 wrapped toolsShow the top 10 only
- govulncheck
- hadolint
- ruff
- kubescape
- actionlint
- shellcheck
- brakeman
- bun
- cargo-audit
- kube-linter
- mobsfscan
- npm
- pip-audit
- pmd
- pnpm
- sslyze
- cargo
- docker
- dockle
- golangci-lint
- guarddog
- kics
- prowler
- testssl.sh
Accessibility
WCAG checks in code, on rendered pages and in Android layouts.
src/components/Hero.tsx:22code.accessibility/img-alt-missingWrapped tools
- lighthouse
- oxlint
- eslint
- pa11y
Performance
Page weight, caching, Core Web Vitals, bundle and image size.
https://example.com/ head > scriptweb.performance/render-blocking-scriptWrapped tools
- lighthouse
- oxlint
- eslint
- pmd
- cargo
SEO
Titles, descriptions, crawlability, sitemaps and broken links.
https://example.com/pricingweb.seo/broken-linkWrapped tools
- lighthouse
Privacy
Trackers before consent, analytics SDKs, personal data in logs.
https://example.com/webapp.browser/tracking-cookie-before-consentWrapped tools
- mobsfscan
Best practices
Repo hygiene, Dockerfile and IaC lint, GitHub Actions hardening.
Dockerfile:7container.dockerfile/add-instead-of-copyWrapped tools
- semgrep
- lighthouse
- checkov
- hadolint
- actionlint
- kube-linter
- kubeconform
- spectral
- tflint
- dockle
All 11 wrapped toolsShow the top 10 only
- kics
Reliability
Type errors, broken pages, redirect chains, missing probes.
k8s/deployment.yaml:18iac.kubernetes/probes-missingWrapped tools
- ruff
- oxlint
- eslint
- tsc
- kubescape
- actionlint
- shellcheck
- biome
- kube-linter
- kubeconform
All 20 wrapped toolsShow the top 10 only
- oasdiff
- phpstan
- pmd
- spectral
- staticcheck
- tflint
- cargo
- golangci-lint
- kics
- mypy
Maintainability
Lint, strict typing, duplication, dead code, huge files.
tsconfig.json:4code.quality/ts-strict-disabledWrapped tools
- ruff
- oxlint
- eslint
- tsc
- biome
- jscpd
- phpstan
- pmd
- staticcheck
- cargo
All 13 wrapped toolsShow the top 10 only
- golangci-lint
- knip
- mypy
Supply chain
Vulnerable dependencies, unpinned versions, licences, image CVEs.
Dockerfile:1container.dockerfile/from-latestWrapped tools
- trivy
- osv-scanner
- zizmor
- grype
- govulncheck
- brakeman
- bun
- cargo-audit
- npm
- pip-audit
All 15 wrapped toolsShow the top 10 only
- pnpm
- scorecard
- tflint
- guarddog
- syft
Compliance
Licence duties, cookie consent, OWASP and CWE mapping, CIS benchmarks.
vendor/parser.c:1code.scancode/strong-copyleftWrapped tools
- prowler
- scancode
- syft
Point it at anything you ship
It detects what you point it at and runs what applies.
Coverage by target and language
By target
| Target | SecuritySec | AccessibilityA11y | PerformancePerf | SEOSEO | PrivacyPriv | Best practicesBP | ReliabilityRel | MaintainabilityMnt | Supply chainSup | ComplianceComp |
|---|---|---|---|---|---|---|---|---|---|---|
Codebasebunx @openaudit/cli . | 34 auditors | 3 auditors | 6 auditors | none | 3 auditors | 6 auditors | 16 auditors | 16 auditors | 17 auditors | 5 auditors |
URLbunx @openaudit/cli https://example.com | 10 auditors | 5 auditors | 2 auditors | 3 auditors | 3 auditors | 4 auditors | 1 auditors | none | none | 2 auditors |
Web appbunx @openaudit/cli https://example.com --browser | 5 auditors | 4 auditors | 1 auditors | 1 auditors | 1 auditors | 1 auditors | 1 auditors | none | none | none |
Containerbunx @openaudit/cli image:nginx:1.27 | 7 auditors | none | 1 auditors | none | none | 4 auditors | 2 auditors | none | 4 auditors | none |
Infrastructure as codebunx @openaudit/cli ./infra | 11 auditors | none | none | none | none | 8 auditors | 8 auditors | none | 5 auditors | none |
Mobile buildbunx @openaudit/cli ./app-release.apk | 5 auditors | 1 auditors | 1 auditors | none | 3 auditors | 1 auditors | none | none | 1 auditors | none |
Cloud accountbunx @openaudit/cli cloud:aws --only cloud | 1 auditors | none | none | none | none | none | none | none | none | 1 auditors |
Bigger dot, more auditors.
By language
| Language | Security | Dependencies | Types, lint and quality |
|---|---|---|---|
| JavaScript / TypeScript | built-in rules, Semgrep | npm, pnpm, Yarn and Bun lockfiles via OSV.dev; npm / pnpm / bun audit | tsc, oxlint (with its React, jsx-a11y and Next.js rules when the project uses them), Biome, ESLint*, knip*, strict tsconfig checks |
| Python | built-in rules, Semgrep, Bandit | requirements*.txt, poetry.lock; pip-audit | ruff, mypy*, type-checker configuration |
| Go | built-in rules, Semgrep, gosec | go.mod; govulncheck* | staticcheck, golangci-lint* |
| Rust | Semgrep | Cargo.lock; cargo-audit | clippy*, [lints] and unsafe policy checks |
| Ruby | built-in rules, Semgrep, Brakeman (Rails) | Gemfile.lock | None |
| PHP | built-in rules, Semgrep | composer.lock | PHPStan |
| Java / Kotlin | built-in rules, Semgrep, mobsfscan (Android) | Maven and Gradle via osv-scanner and Trivy | PMD (Java) |
| C# / .NET | built-in rules, Semgrep | NuGet via osv-scanner and Trivy | None |
| Swift / Objective-C | mobsfscan (iOS) | None | None |
| Shell | None | None | ShellCheck, set -euo pipefail checks |
| HTML, CSS, JSX, Vue, Svelte | accessibility and performance rules | None | None |
* Opt-in: run it with --only <id>, e.g. --only code.clippy. The next section explains why some tools are opt-in.
One issue, one finding
Many tools, one result.
Run
Point it at a folder, URL, image or cloud account. Missing tools are skipped.
Merge and score
Duplicates merge into one finding. Each area scores 0 to 100.
One leaked key, three tools, one finding.
Report and gate
HTML, JSON, SARIF, Markdown or CSV.
--fail-onfails the CI run.
A report people actually read
One HTML file. Works offline, prints cleanly.
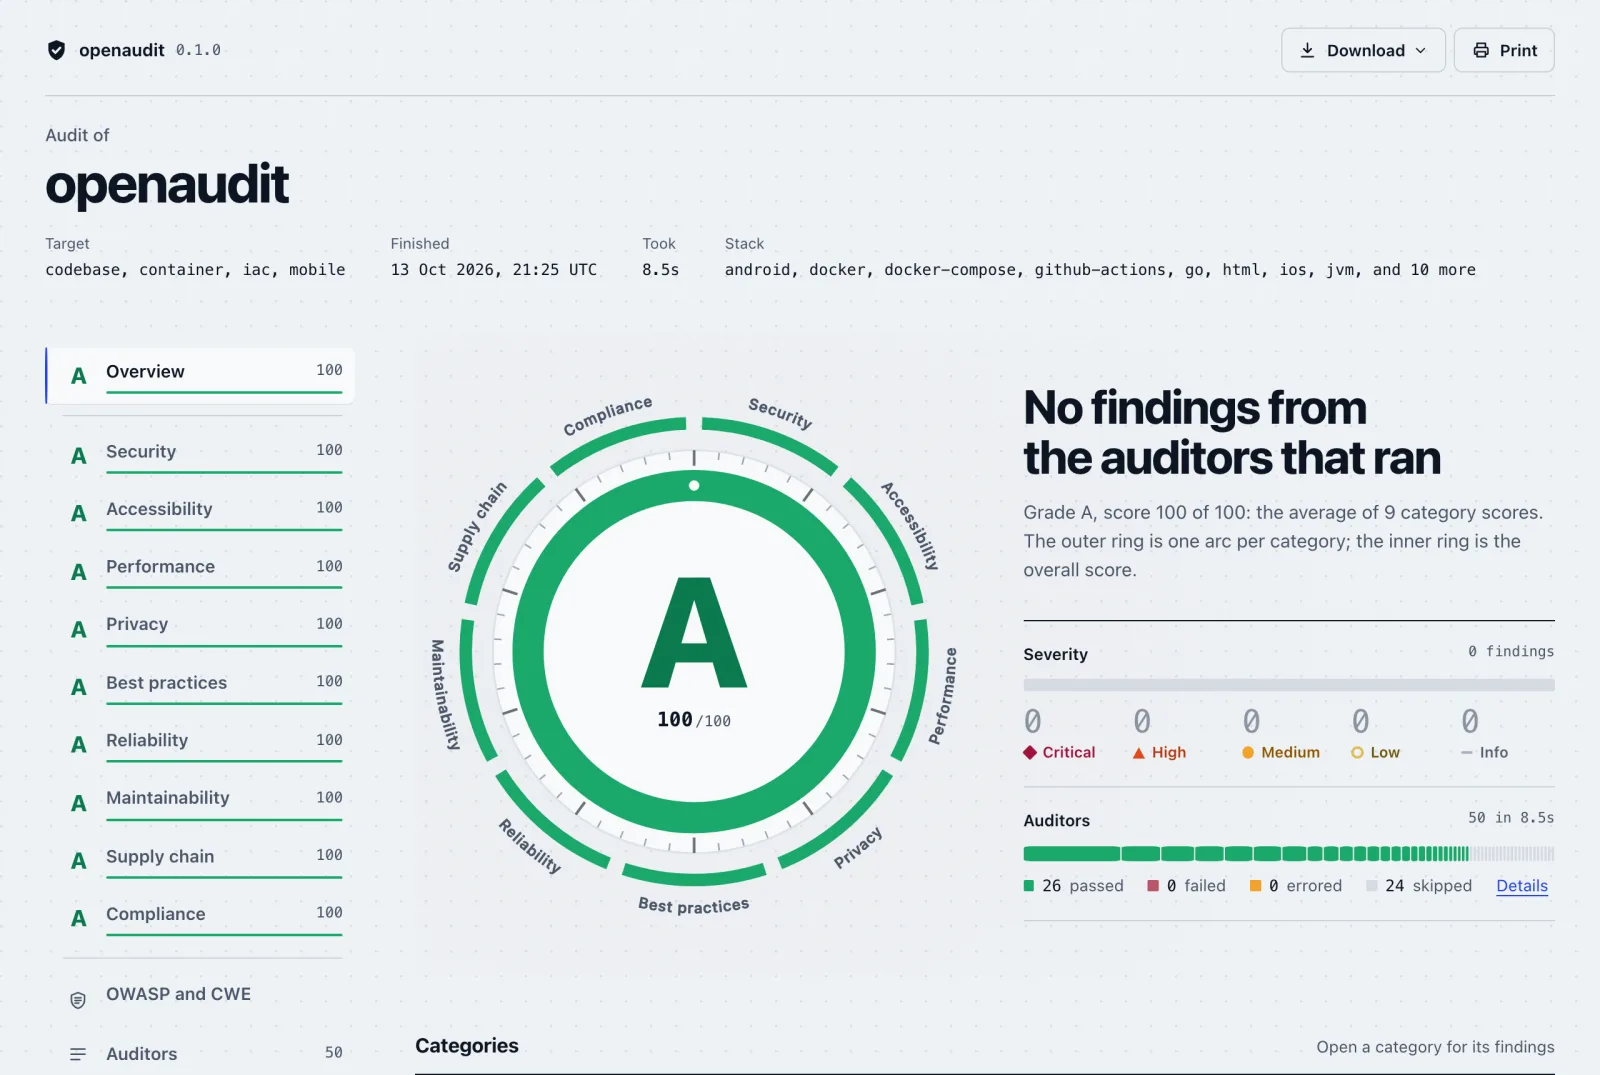
 Open the live report
Overview
One grade, one arc per area.
A tab per area
Filters, search, findings by rule.
OWASP and CWE
Mapped to both top lists.
Downloads
HTML, JSON, SARIF, Markdown or CSV.
Runs where you already work
Same report from every route.
bunx @openaudit/cli .                            # a codebase
bunx @openaudit/cli https://example.com          # a live site (add --browser for Playwright + axe-core)
bunx @openaudit/cli ./app-release.apk            # a mobile build (.apk, .aab, .ipa)
bunx @openaudit/cli image:nginx:1.27             # a container image
bunx @openaudit/cli cloud:aws --only cloud       # a live cloud account (Prowler)

bunx @openaudit/cli . -f html -o report          # write the interactive report to report/
bunx @openaudit/cli doctor # which optional scanners are installedclaude mcp add openaudit -- bunx @openaudit/cli mcppermissions:
contents: read
security-events: write
steps:
- uses: actions/checkout@v7
with:
fetch-depth: 0 # diff mode compares against the base branch
- uses: wezter96/openaudit@main # pin to a commit SHA in real use
with:
fail-on: high# Audit the current directory. Run as yourself: git refuses repositories owned by
# another user, and reports are written as you
docker run --rm --user "$(id -u):$(id -g)" -v "$PWD:/src" -w /src \
ghcr.io/wezter96/openaudit . -f html,sarif -o openaudit-report --fail-on high
# Audit a live site with a real browser
docker run --rm ghcr.io/wezter96/openaudit:latest-full https://example.com --browser
# See which tools are installed
docker run --rm ghcr.io/wezter96/openaudit doctorinclude:
- remote: https://raw.githubusercontent.com/wezter96/openaudit/main/integrations/gitlab/openaudit.gitlab-ci.yml
variables:
OPENAUDIT_FAIL_ON: high # optionalrepos:
- repo: https://github.com/wezter96/openaudit
rev: main # pin to a tag or commit
hooks:
- id: openaudit # needs Bun on PATH
# - id: openaudit-docker # or: the Docker image, nothing else to install- uses: wezter96/openaudit@<sha>
with:
fail-on: high
# Trusted on pushes, where the file is what was merged or pushed by someone
# with write access. On pull_request and pull_request_target the PR can edit it.
config: ${{ github.event_name == 'push' && 'openaudit.config.jsonc' || '' }}- uses: oven-sh/setup-bun@v2
- name: openaudit
run: bunx @openaudit/cli . --format sarif,markdown --out openaudit --fail-on high
- name: Upload SARIF
if: always()
uses: github/codeql-action/upload-sarif@v4
with:
sarif_file: openaudit/openaudit-report.sarif
category: openaudit
- name: Job summary
if: always()
run: cat openaudit/openaudit-report.md >> "$GITHUB_STEP_SUMMARY"{
"mcpServers": {
"openaudit": { "command": "bunx", "args": ["@openaudit/cli", "mcp"] }
}
}Safe on hostile input
Every target is treated as hostile. Nothing it scans gets built or run.
Five guards against hostile targets
Files
Reads stay in the project. Symlinks out are never followed.
HTTP
Your headers go only to the target. Redirects drop credentials.
Agents
Its own agents get no shell. The browser stays on the target.
Wrapped tools
Nothing gets built or installed. Linters that run code are opt-in.
Git
Hooks and fsmonitor are off. Diffs compare commits.